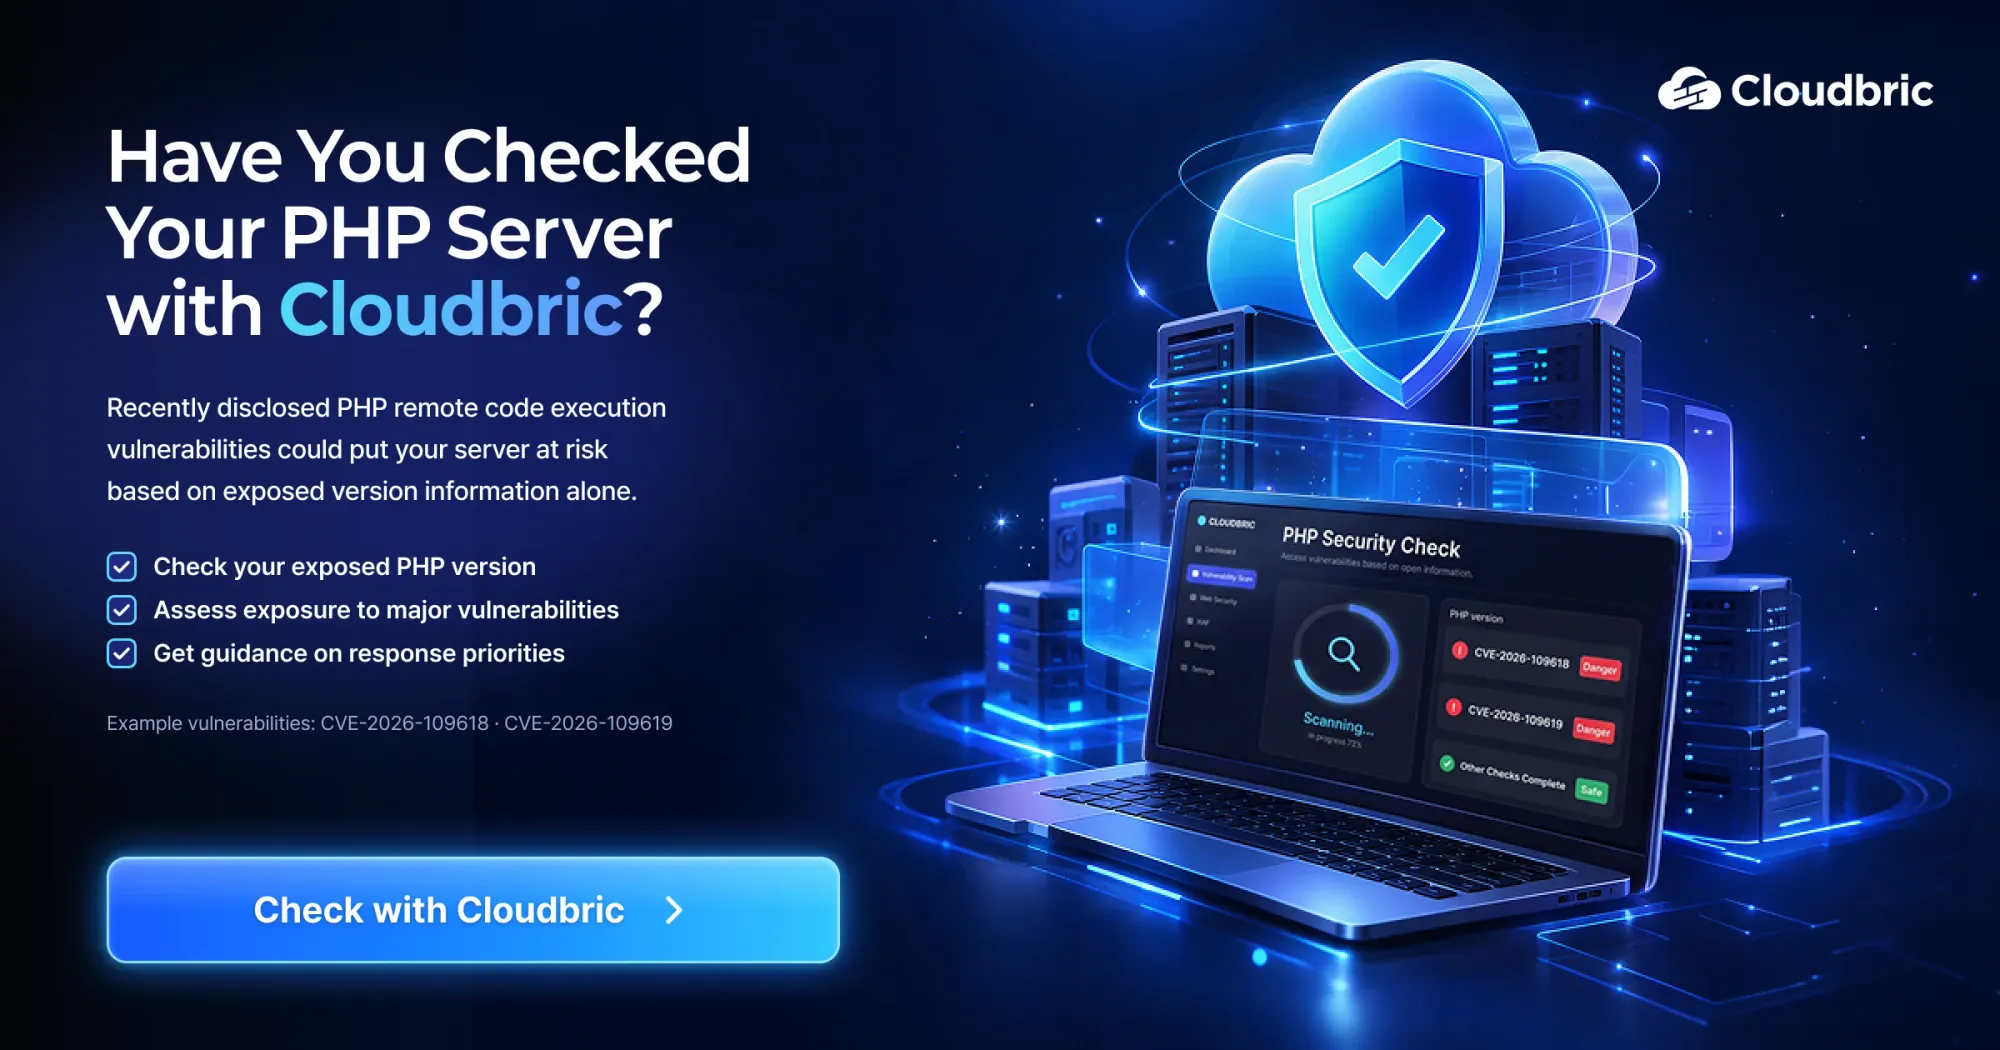
Penta Security is moving to mitigate the risks posed by the recently disclosed PHP2Shell remote code execution vulnerabilities through new diagnostic and defensive tools. The company has launched the Cloudbric Security Check service to help organizations identify external PHP version exposure. This development addresses CVE-2026-109618 and CVE-2026-109619, which allow unauthenticated attackers to execute code on vulnerable systems.
Cloudbric Security Check and PHP2Shell Diagnostics
The Cloudbric Security Check service provides a non-intrusive method for organizations to assess their vulnerability status by simply entering a website URL. The tool analyzes server response information to identify exposed PHP versions and assess potential impact without attempting to exploit the vulnerabilities. For environments where external identification is insufficient, Penta Security offers an assessment script to check internal PHP versions and specific configuration settings. This diagnostic approach aims to provide users with prioritized remediation guidance, including software updates or temporary mitigation steps. The service is currently accessible via the Penta Security and Cloudbric websites in English, Korean, and Japanese, allowing for rapid, software-free exposure assessment across diverse web infrastructures.
WAPPLES and Cloudbric WAF+ Defensive Integration
To provide immediate protection, Penta Security has integrated specific response rules into its existing security product ecosystem. Customers utilizing the WAPPLES intelligent web application firewall have received custom rules and configuration guidance designed to block exploitation attempts. Simultaneously, the company has applied these relevant response rules to its SaaS-based web security service, Cloudbric WAF+. While the primary recommendation for addressing these vulnerabilities is updating to a patched PHP version, Penta Security is positioning its WAF solutions as a critical layer for organizations unable to perform immediate patching. These defensive measures are intended to mitigate risk by blocking malicious requests that target the specific flaws identified in the PHP2Shell disclosure.
Key Takeaways
- The Cloudbric Security Check service allows users to assess PHP version exposure via URL without software installation.
- Penta Security has deployed custom response rules for both WAPPLES WAF customers and the Cloudbric WAF+ SaaS service.
- The PHP2Shell vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, permit unauthenticated remote code execution.
TechInsyte's Take
In our view, Penta Security’s dual-track approach—combining rapid external diagnostics with immediate WAF rule deployment—highlights the increasing necessity for layered defense-in-depth. By providing a non-intrusive check alongside specialized WAF rules, the company is addressing the reality that enterprise patching cycles often lag behind vulnerability disclosures. This strategy suggests that for modern digital infrastructure, the ability to implement temporary, automated mitigation via a WAF is just as critical as the eventual permanent patch, especially as automated attack vectors continue to evolve.
Questions & Answers
How can organizations quickly determine if they are vulnerable to PHP2Shell?
Organizations can use the Cloudbric Security Check service by entering their website URL to identify exposed PHP versions or utilize Penta Security's assessment script for deeper internal configuration checks.
What is the recommended long-term remediation for CVE-2026-109618 and CVE-2026-109619?
The fundamental response is to update the server to a PHP version where these specific vulnerabilities have been officially fixed.
How does Penta Security support organizations that cannot patch immediately?
Penta Security provides custom response rules for WAPPLES and Cloudbric WAF+ to block exploitation attempts, acting as a temporary mitigation layer until patches can be applied.
Does the Cloudbric Security Check tool pose a risk to the target server?
No, the service uses a non-intrusive assessment method that checks server response information without attempting to exploit any vulnerabilities.
Source: Penta Security